EmbeddingGemma 2: an open, lightweight multimodal embedding model
deepmind.google·6d ago
TL;DR
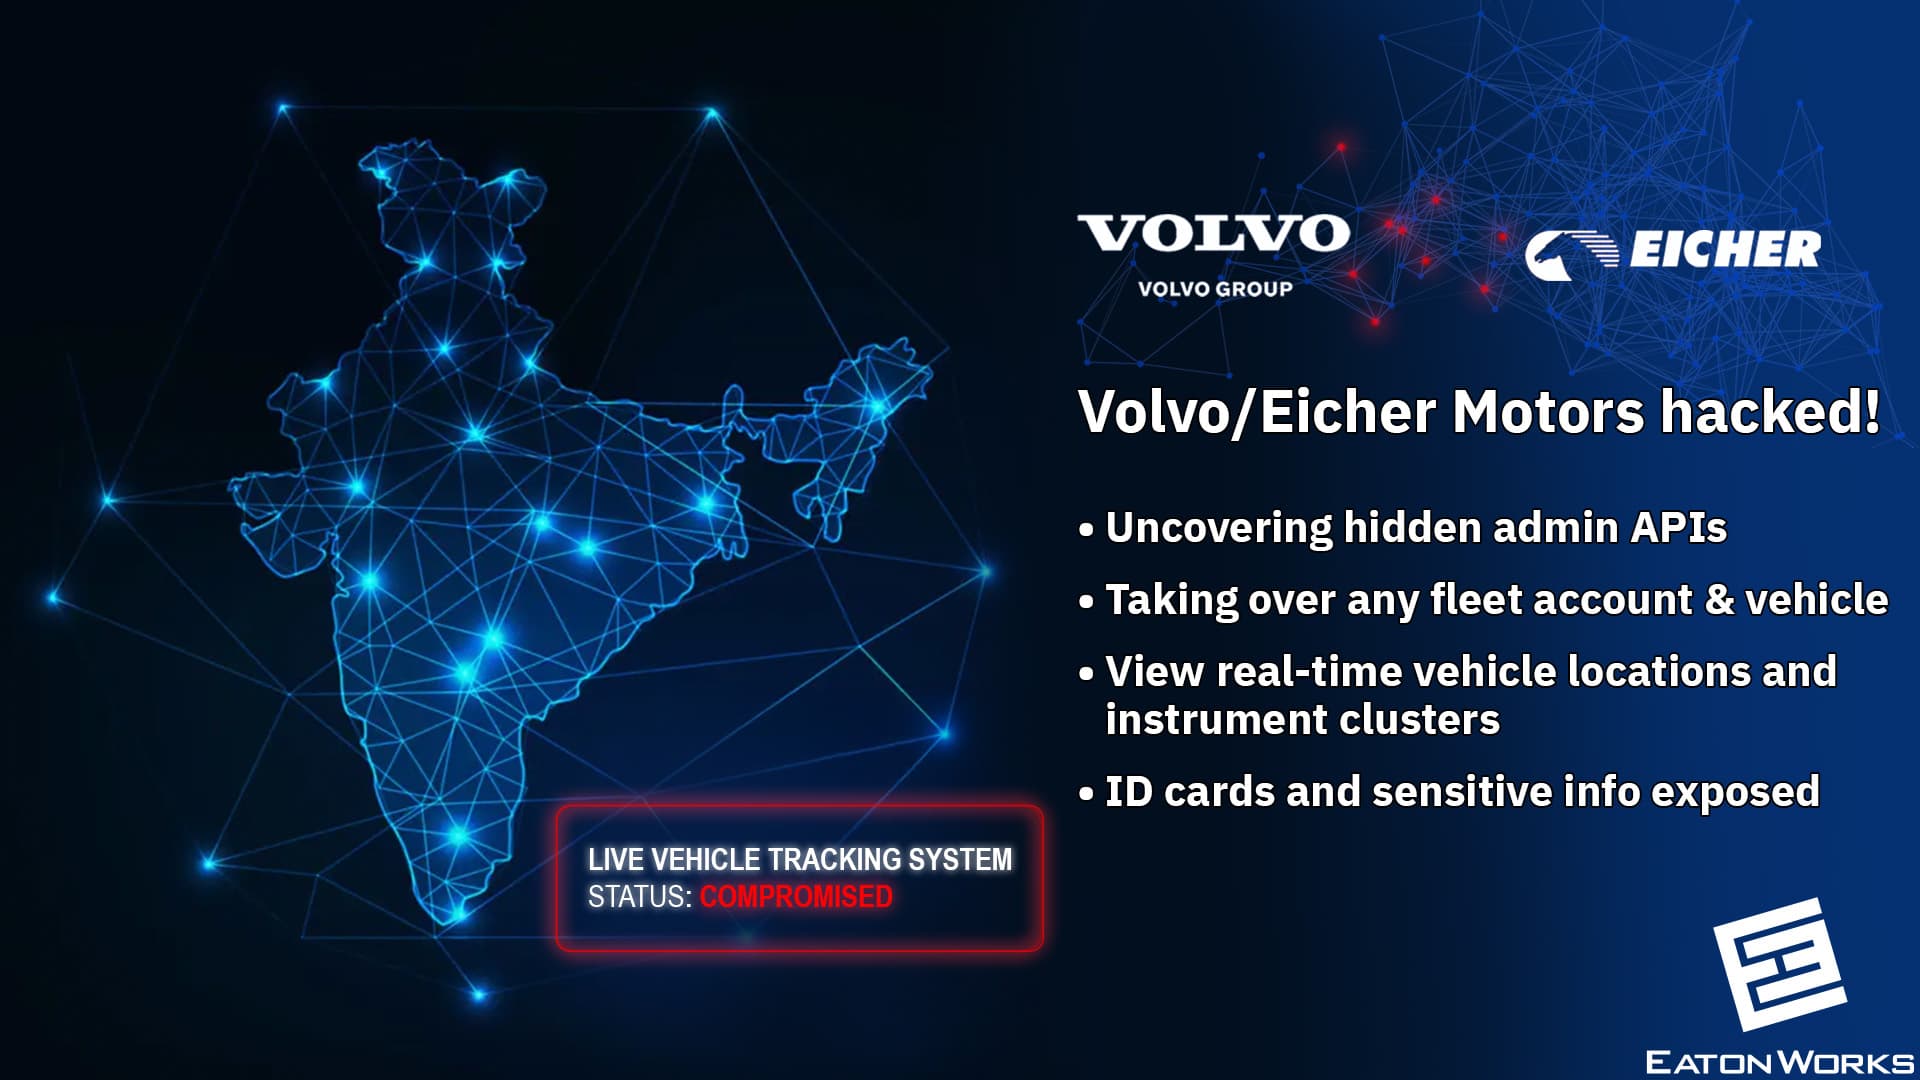
A vulnerability in Volvo/Eicher's My Eicher fleet management platform was discovered, allowing unauthorized access to internal APIs and potential account takeovers. This could enable control over entire fleets of vehicles, posing significant security risks.
✦ Why It Matters
Review and strengthen API security protocols in your fleet management systems immediately.
Key Takeaways
Full Summary
My Eicher, a fleet management system for commercial vehicles in India, was found to have a significant security flaw in its APIs. This vulnerability exposed unauthenticated internal APIs, enabling access to sensitive user information and the ability to take over accounts.
The researcher discovered a list of 748,000 customers and 676,000 vehicles, along with access to 2.5 million one-time passwords (OTPs) dating back to 2021. By exploiting these APIs, the researcher could gain control over entire fleets, which could include hundreds of vehicles.
Additionally, sensitive documents such as Aadhaar cards and driving licenses were also exposed. After reporting the vulnerability, it was fixed within weeks, but the researcher faced challenges in communicating further concerns to the company.
Related