EmbeddingGemma 2: an open, lightweight multimodal embedding model
deepmind.google·6d ago
TL;DR
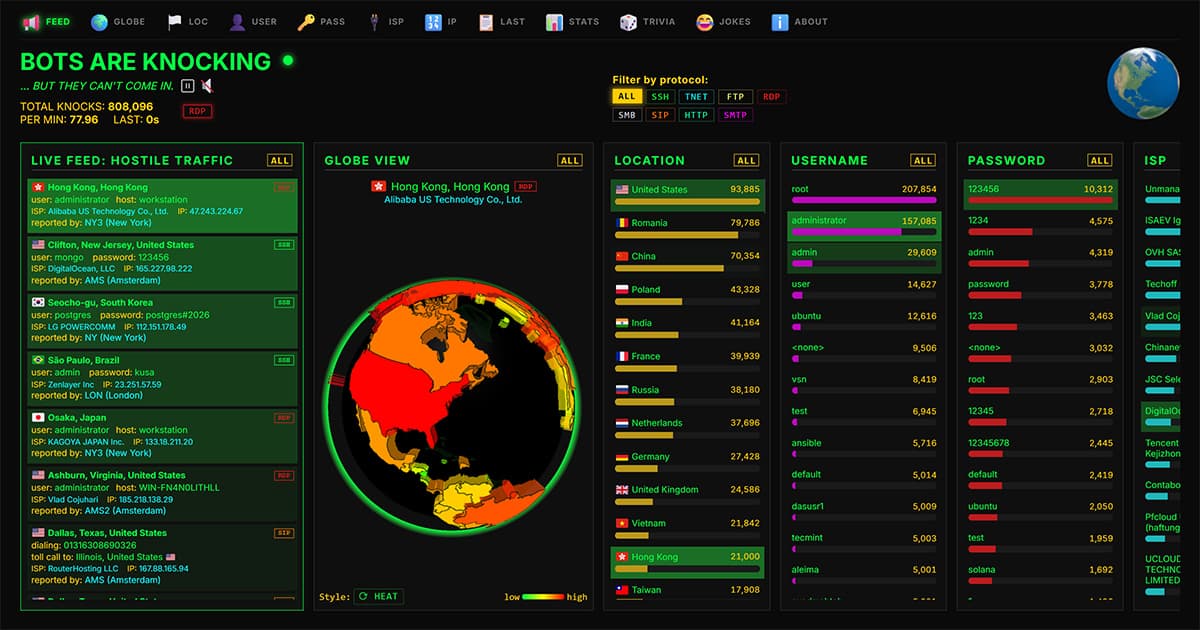
A coordinated phone-fraud attack involving Citigroup, Idaho, and Build-A-Bear targeted a VoIP server, exploiting it for International Revenue Share Fraud. The incident highlights vulnerabilities in corporate networks due to bot infections.
✦ Why It Matters
Ensure your network security protocols are robust to prevent bot infections and potential fraud.
Key Takeaways
How It Works
The attack exploited the VoIP server by using it as an open relay to dial premium-rate numbers. Each compromised machine in the botnet received commands to target the same number, indicating centralized control.
This method allows attackers to profit from calls made through infected networks.
Related