EmbeddingGemma 2: an open, lightweight multimodal embedding model
deepmind.google·6d ago
TL;DR
CISA has issued an urgent warning about the vulnerabilities of operational technology (OT) exposed to the public Internet, urging immediate action to enhance security. Key recommendations include removing OT from the Internet, changing default passwords, and improving authentication measures.
✦ Why It Matters
Immediately review and strengthen your OT security measures to prevent potential cyber threats.
Key Takeaways
Full Summary
CISA's alert highlights the critical risks posed by operational technology (OT) connected to the public Internet, where devices face relentless automated attacks. The recommendations are clear: organizations must act immediately to sever OT connections, change default passwords, and enhance network protections.
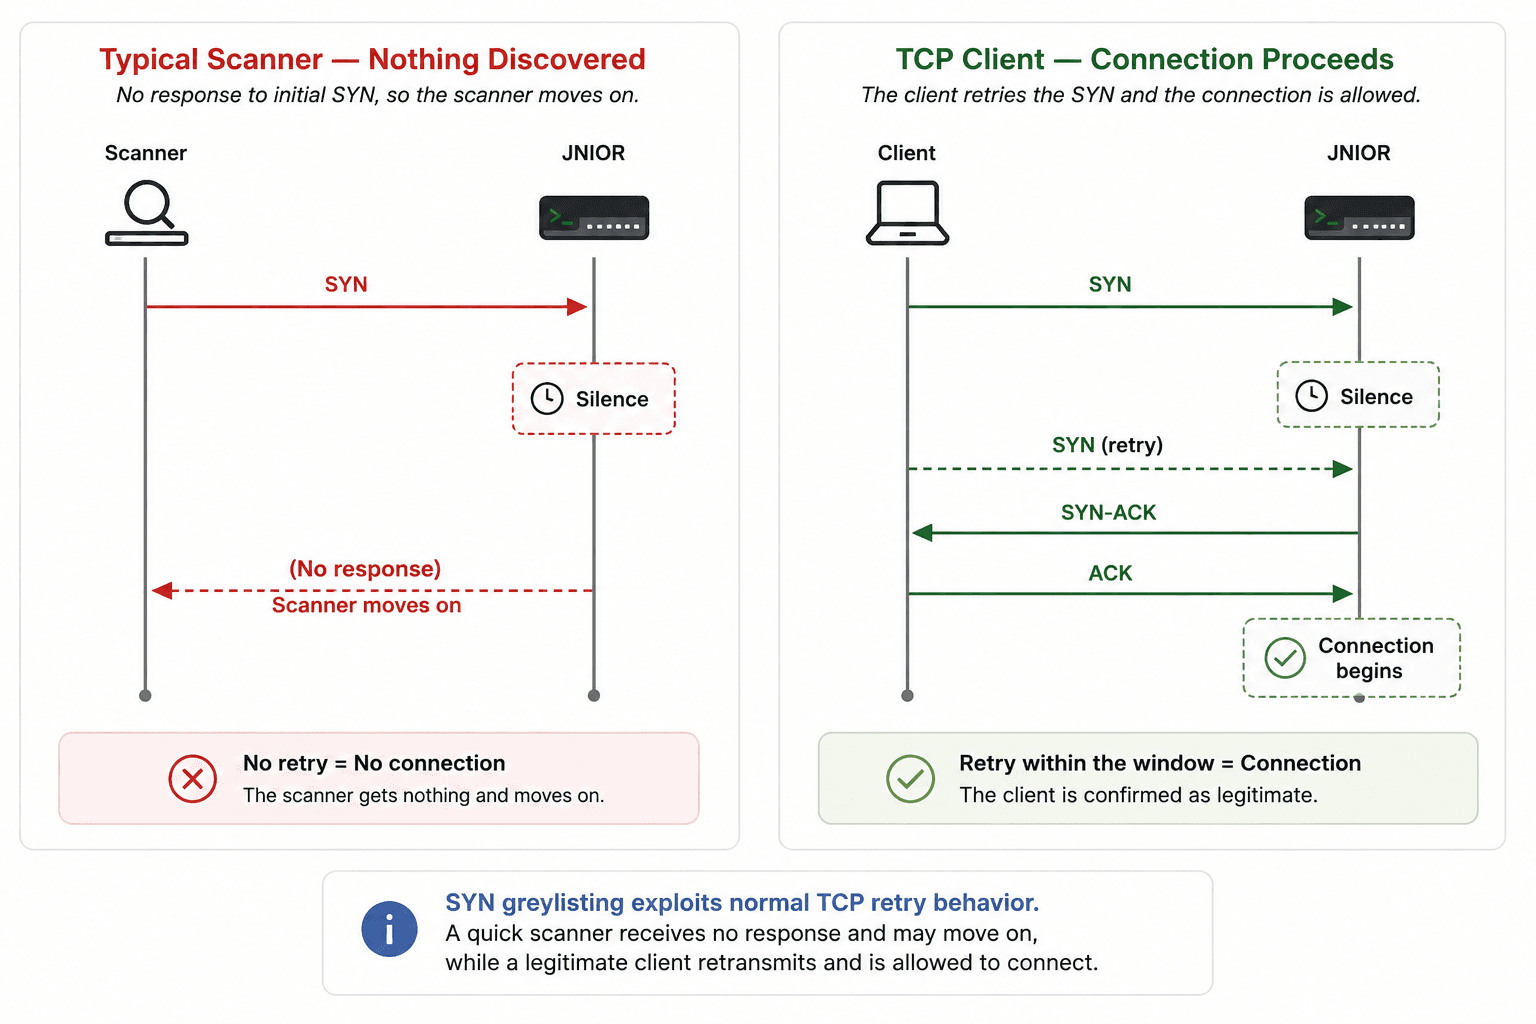
However, simply cutting off communication isn't always feasible due to the increasing need for OT connectivity. The article emphasizes the importance of defensive techniques that minimize attackers' opportunities without heavily taxing system resources.
Observations from the JANOS operating system, used in JNIOR devices, reveal that even strong login credentials can be compromised by sustained attacks that consume processing power, potentially leading to denial-of-service (DoS) scenarios. This calls for a broader discussion on effective security measures that balance connectivity and protection.
Related