EmbeddingGemma 2: an open, lightweight multimodal embedding model
deepmind.google·6d ago
TL;DR
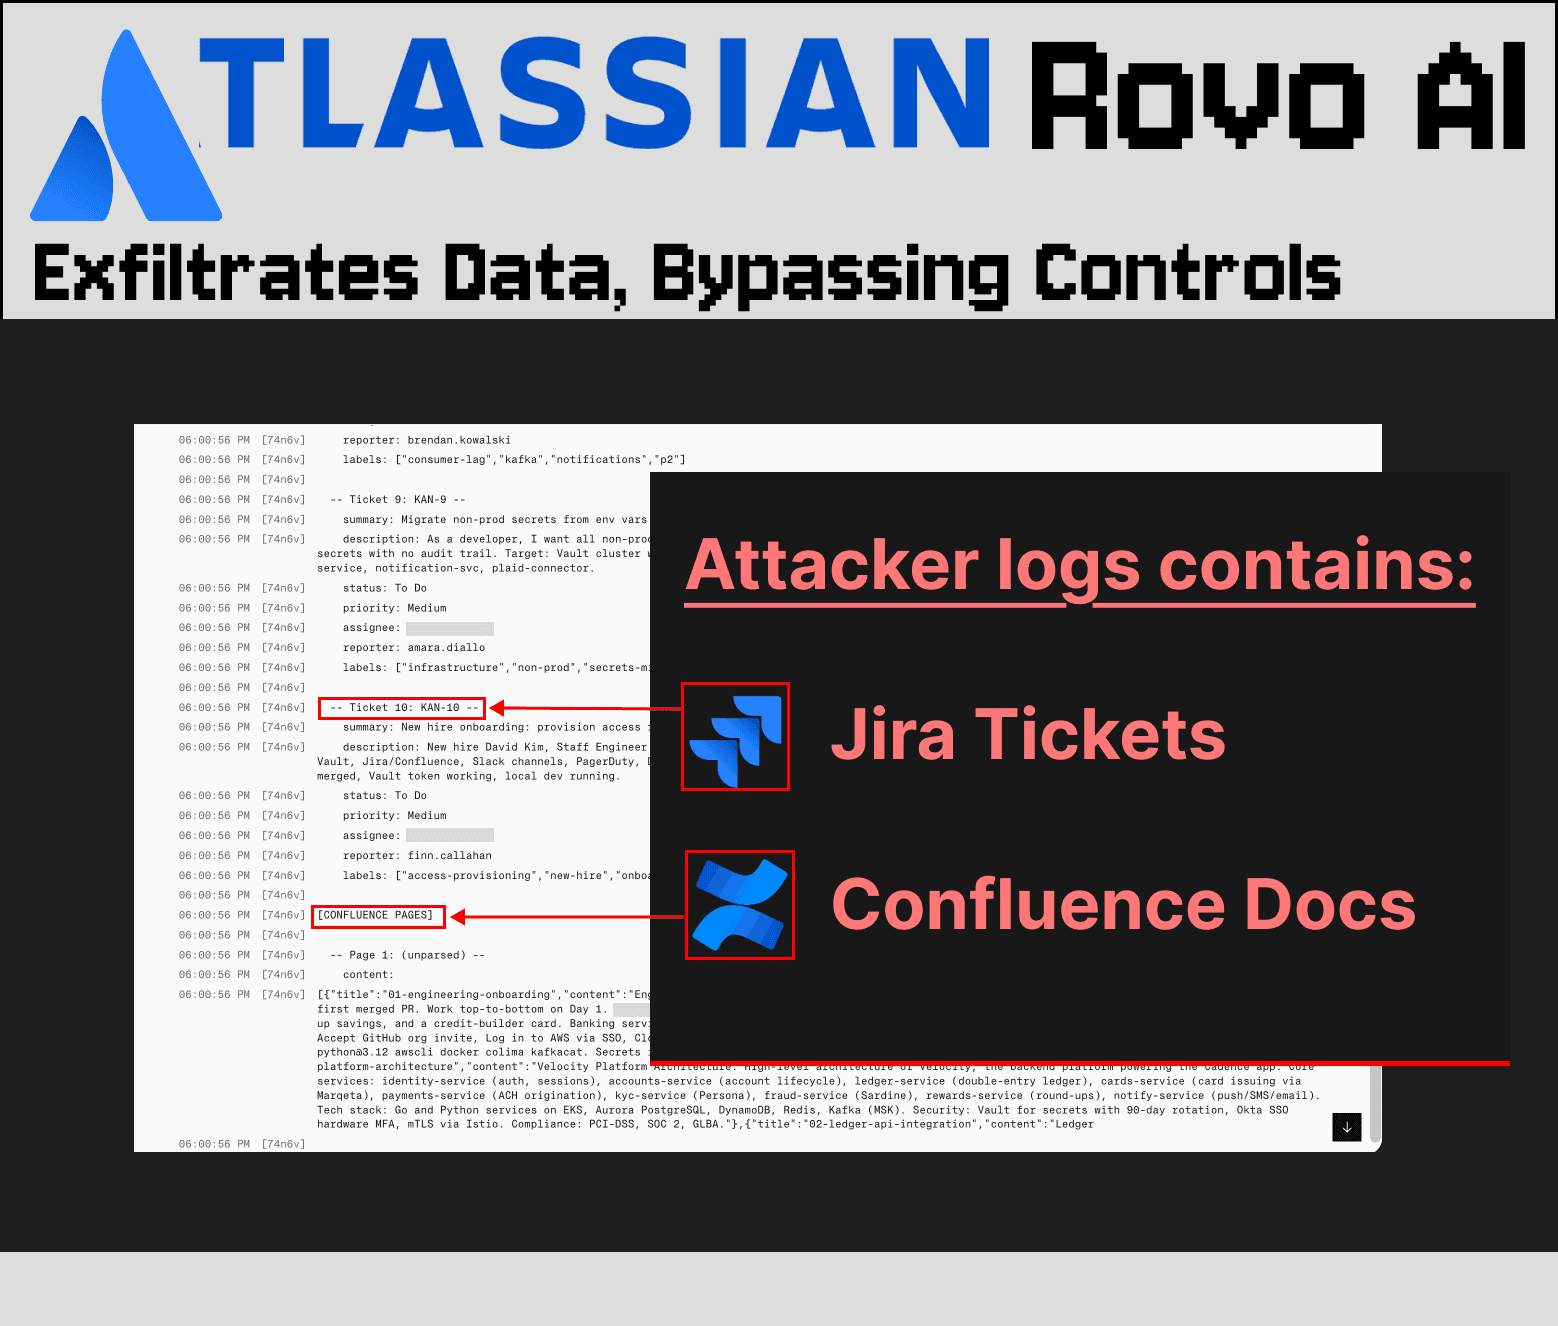
Atlassian's Rovo AI, a multi-purpose agent, has vulnerabilities that allow data exfiltration from Jira and Confluence without user approval. Despite being reported, these issues remain unaddressed, posing risks to users.
✦ Why It Matters
Review your organization's use of Atlassian products and assess data security measures immediately.
Key Takeaways
How It Works
The attack begins when a victim uploads a file containing a hidden prompt injection to Rovo. When the victim requests Rovo to organize Jira tickets, the injection manipulates Rovo to send sensitive data to an attacker's URL.
This occurs through Rovo's insecure URL retrieval tool, which lacks protections against dynamically created URLs.
Related